Mad World | Browser Extension & API
Passbolt 5.17.0 "Mad World" introduces passkeys for multi factor authentication, improves autofill reliability across websites, makes permission changes easier to review when moving resources, and brings PIN code resources to QuickAccess. This release also includes security hardening and performance improvements.
Passkeys for MFA
Passbolt 5.17 adds passkeys as a second authentication factor, alongside the TOTP, Yubikey OTP and Duo providers that are already supported. It answers a requirement that many organisations now include in their procurement processes: multi-factor authentication that resists phishing, which one-time codes cannot provide.
Built on the WebAuthn/FIDO2 standard, it is bound to the domain of the Passbolt instance, and the browser refuses to use it anywhere else, so a lookalike site has nothing to capture. Basically, one-time code can be typed into a fake login page and relayed to the real site by an attacker. Passkeys cannot be used this way and protects against this kind of phishing.
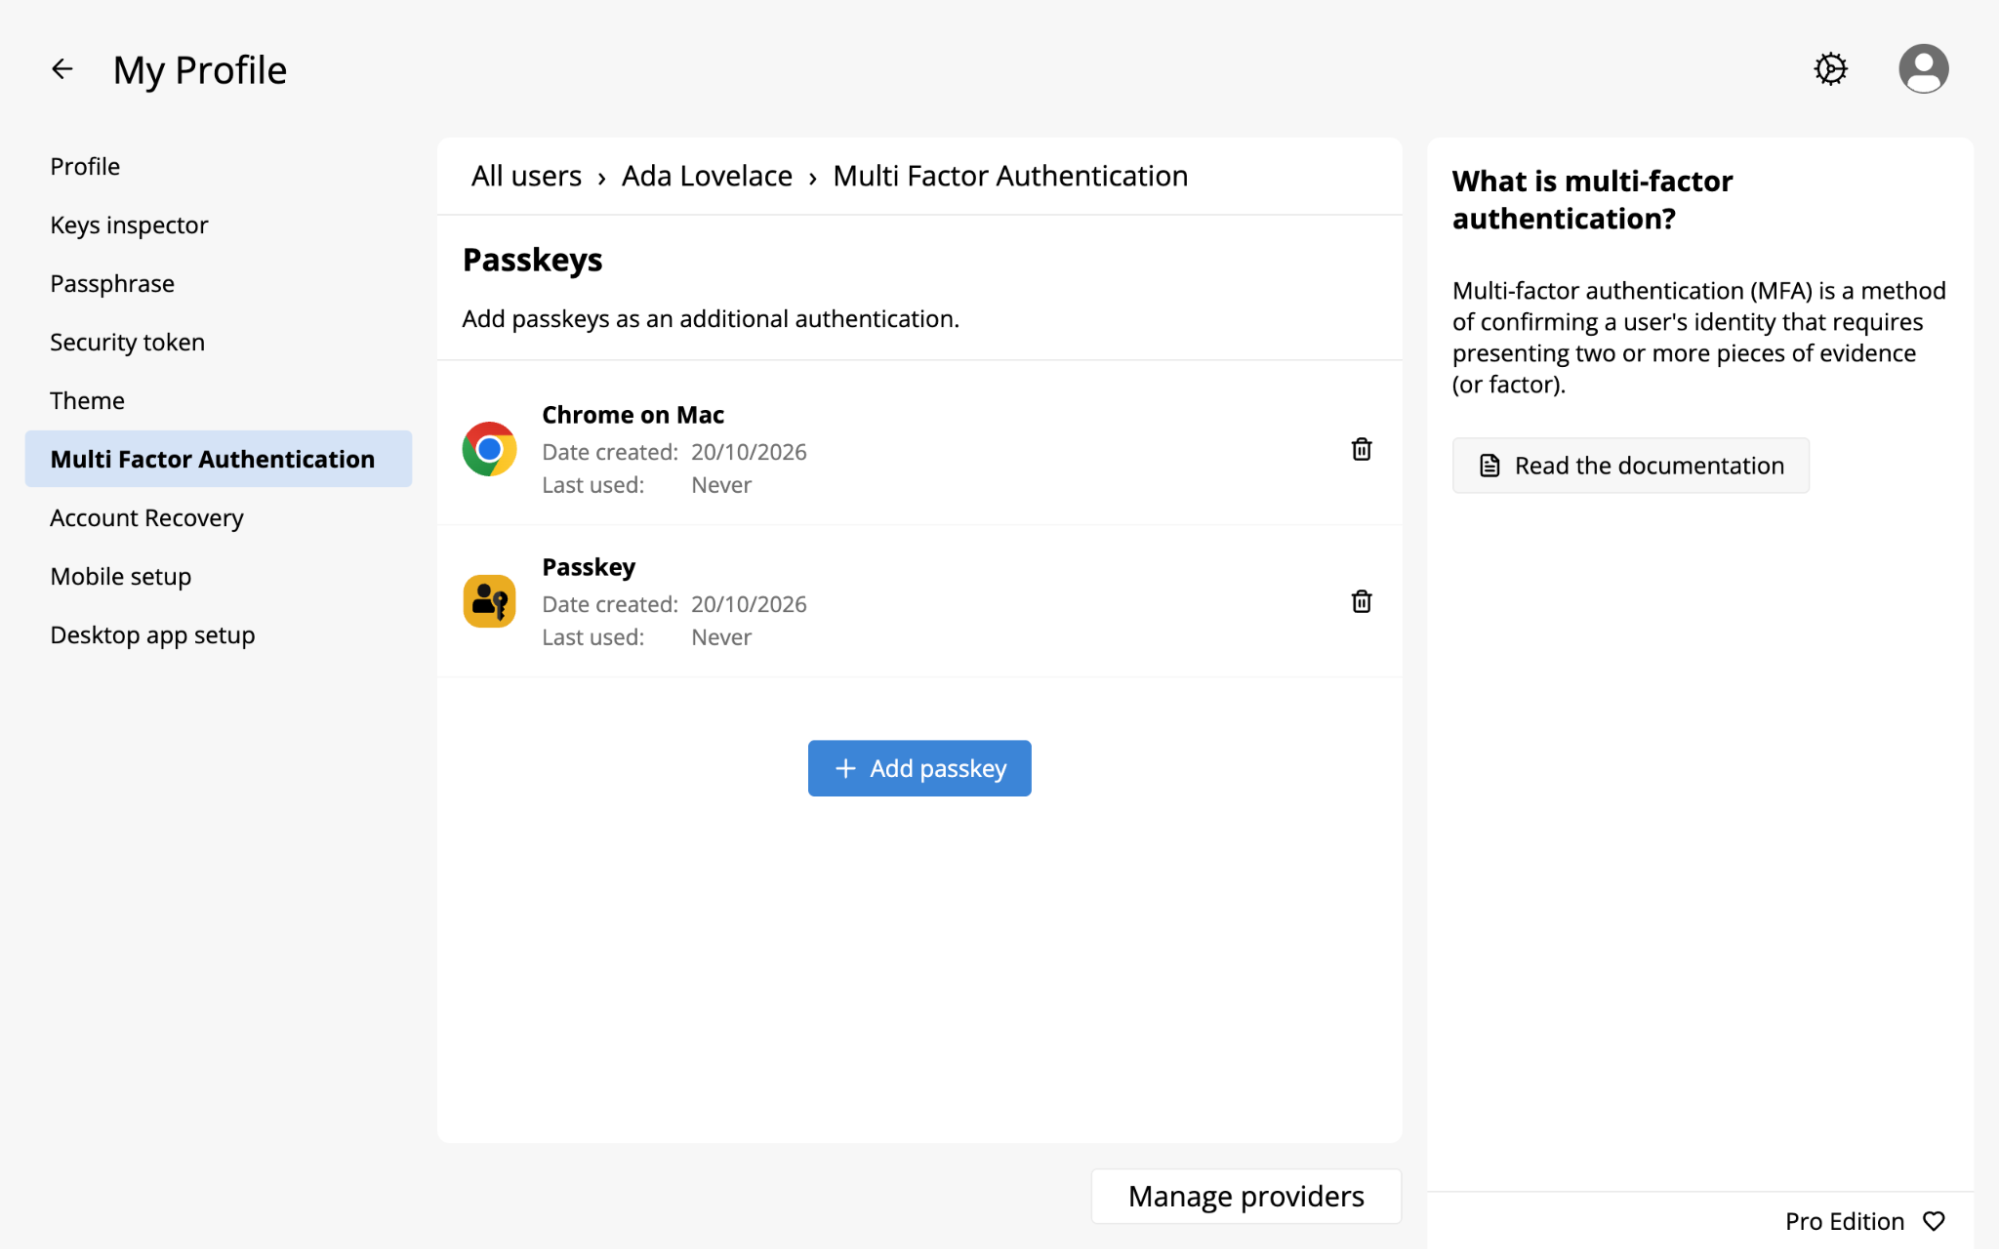
Passkeys are available in every edition. Once an administrator enables them in Administration > Multi-factor authentication, each user can register up to ten passkeys from Profile > Multi-factor authentication, using a security key such as a YubiKey or the biometrics built into their laptop, phone, such as Touch ID or Windows Hello.
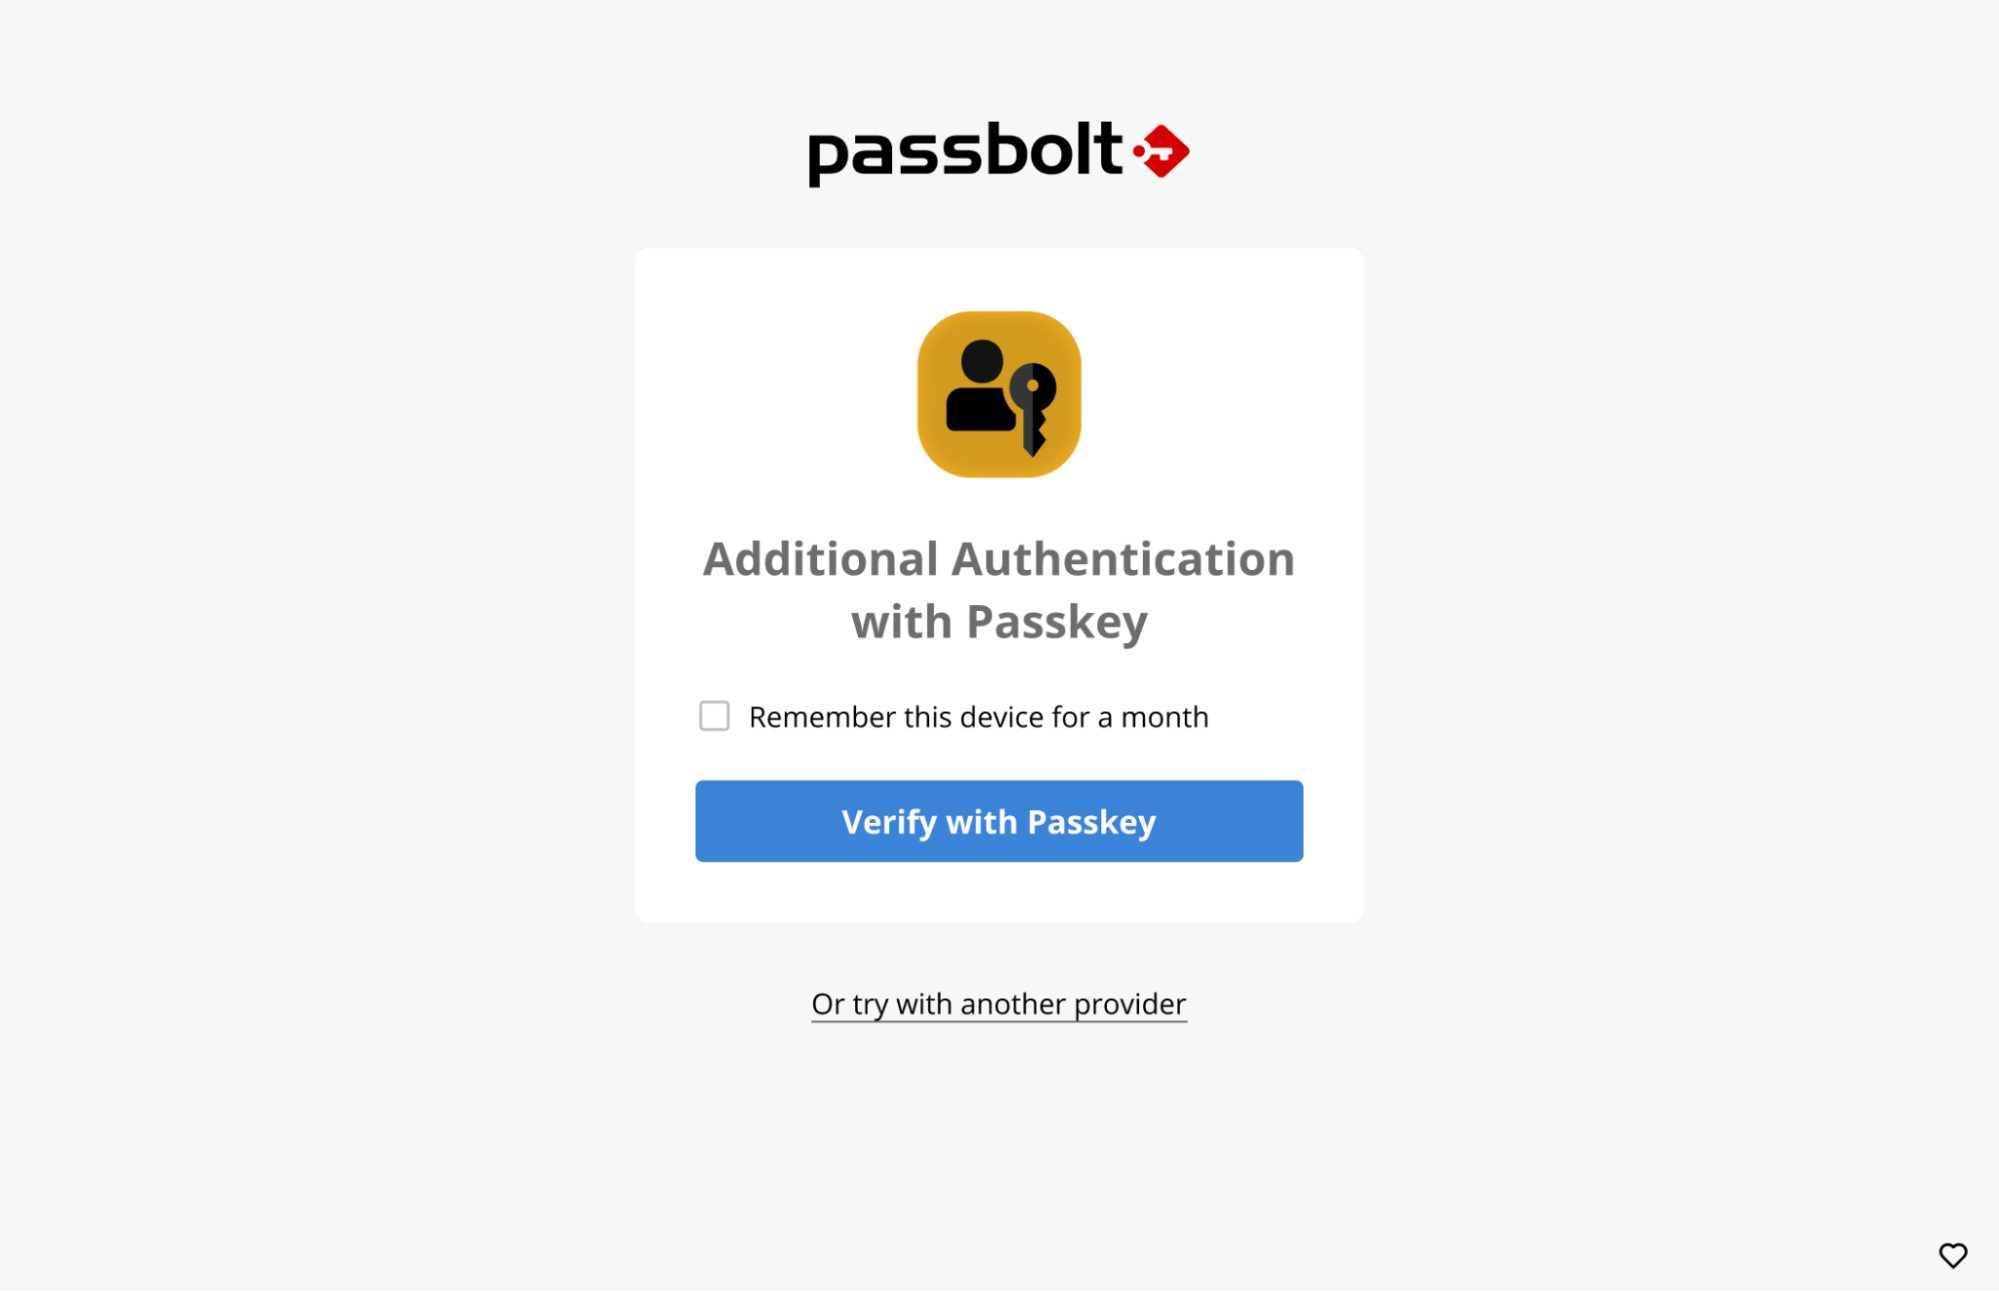
From then on, Passbolt asks for the passkey right after sign-in, as it does for the other providers. Users can tick "Remember this device for a month" to skip the check on a trusted device, or leave it unticked to verify every time. Organisations using Passbolt Pro edition, and wanting a stricter posture can disable this option in the Multi-factor authentication policy settings, so that every sign-in requires the passkey.
This first step covers multi-factor authentication. Storing passkeys for third-party websites as a resource type and Passwordless sign-in to Passbolt will follow in upcoming releases.
A new autofill detection engine
Autofill is a core part of the Passbolt browser experience, and version 5.17 rebuilds its detection engine from scratch. It tackles two familiar frustrations: no autofill on a form that clearly needs it, and an autofill icon in a field that has nothing to do with credentials.
Getting this right is harder than it looks, because no two websites build their forms the same way. Field names differ, labels come in many languages, and the underlying code varies widely from one site to the next. A handful of regular expressions could only go so far, and the previous engine had reached its limits.
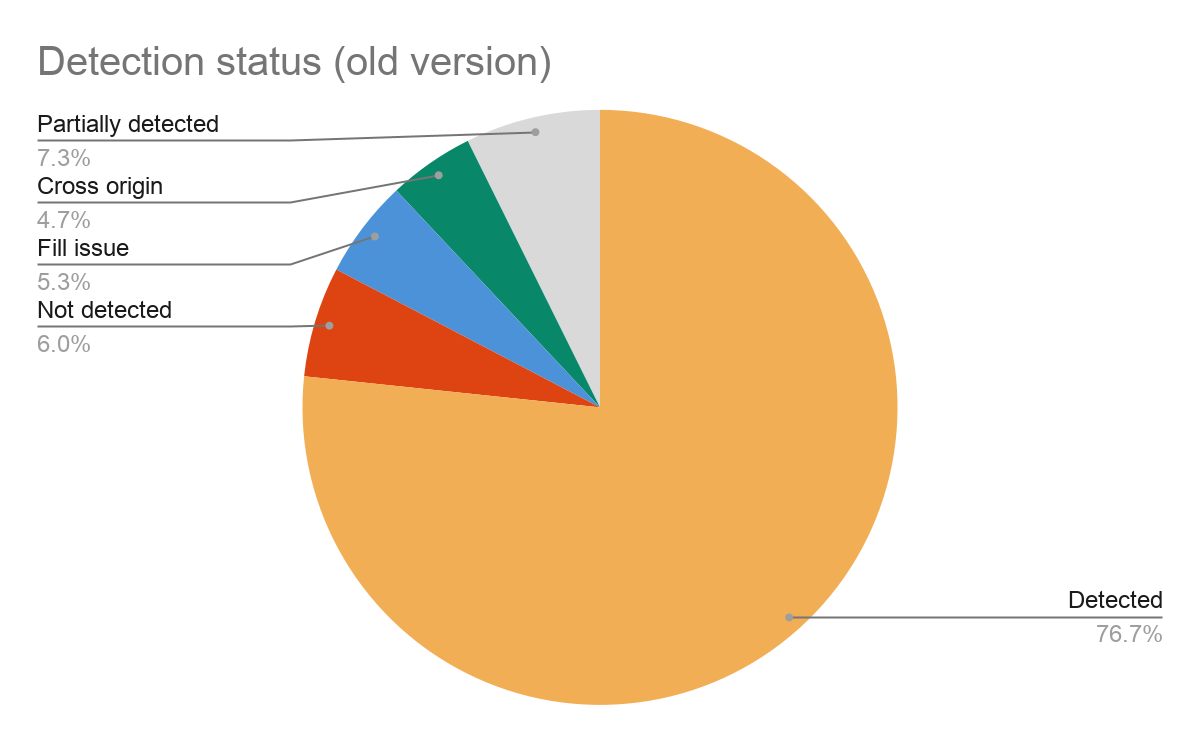
The new engine understands the context of each field, from the structure of the form to the labels around it, before deciding whether to step in. The first benchmarks are very promising: on our internal test set, form detection rises from 74% with the previous engine to 93.4%, while processing cost stays low.
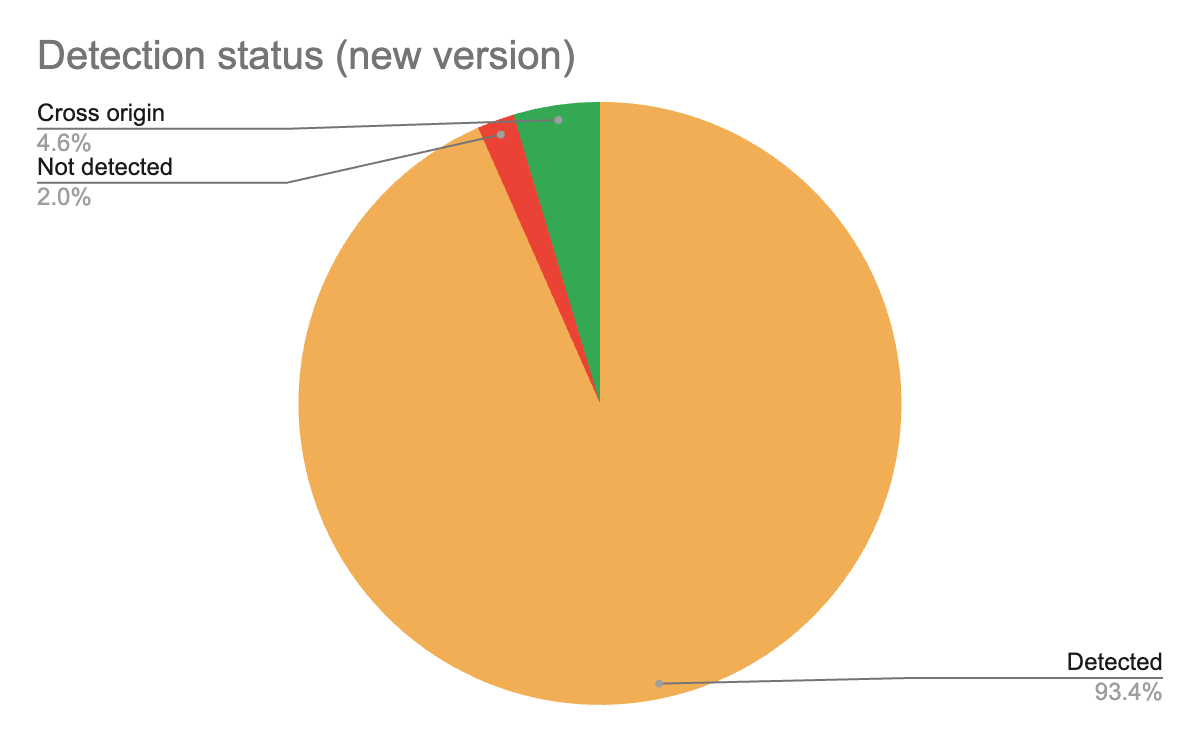
A test set is not the web, though, and this is where the community comes in: we are eager to hear how the engine behaves on the websites our users rely on every day. For those curious about the inner workings, a detailed blog post will follow.
Safer permission handling during resource moves
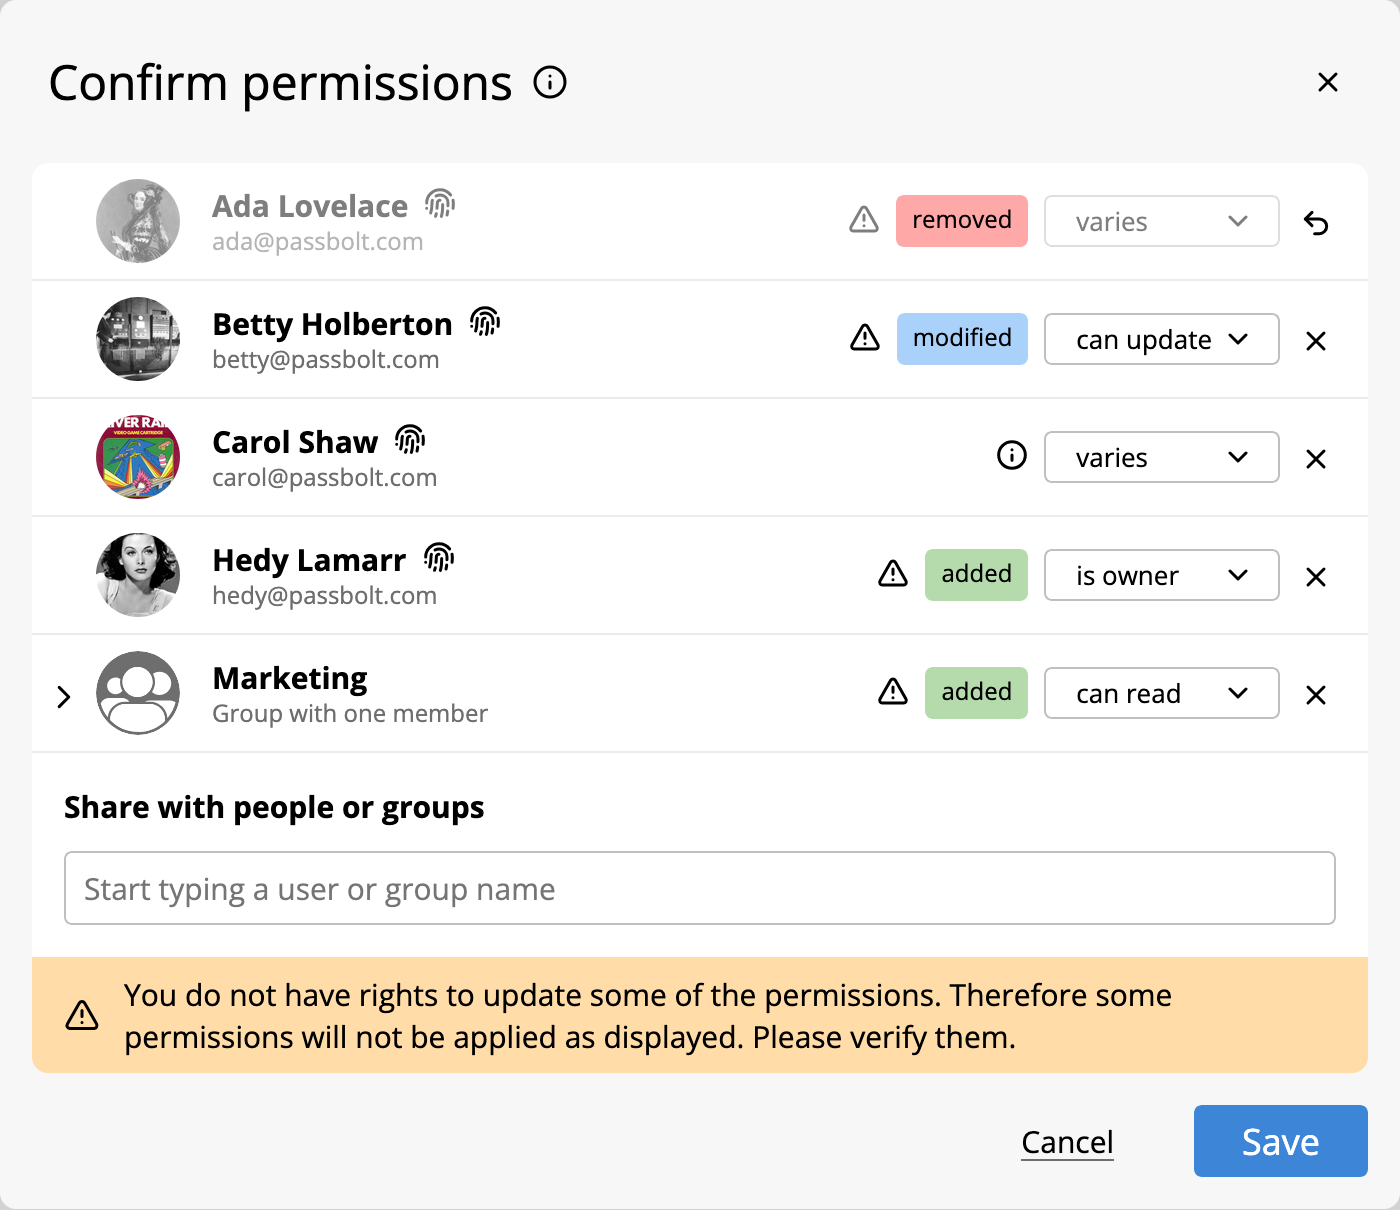
Passbolt 5.17 brings the permission review introduced in 5.14 to moves of resources and folders. Creating a resource in a shared folder, editing a shared resource and now moving items all ask for the same explicit confirmation.
A move needs this step because placing a resource in a shared folder, or taking it out of one, can change who has access to it. Previously, users chose between keeping the current permissions and applying those of the destination folder, without seeing what either option would produce. Getting it right meant anticipating the outcome, which could be confusing.
From this version, every move follows the destination folder strategy: permissions inherited from the folder the items leave are removed, and those of the destination folder take their place. Before saving, Passbolt shows who will gain, lose or keep access, and this proposal can be refined with the usual granular control, one user or group at a time. Nothing changes until the user confirms, and the operation can still be cancelled.
Access PIN Codes through QuickAccess
This release brings PIN codes to QuickAccess. Users no longer need to switch to the web workspace to retrieve door codes or device PINs.
PIN codes also inherit offline availability, using the same security and synchronization controls as other secrets, as described in the Offline Mode blog post.
This is part of a broader effort to expand QuickAccess and Offline Mode support to all remaining resource types in upcoming releases.
Improved group management performance for large organisations
The release also tackles one of the most requested improvements on adding a user to a large group with many shared resources. This operation is now more than twice as fast and is achieved through optimizing the underlying database queries. This cuts the wall time for adding a user to a group having access to 300 resources from 1.19 seconds to 514 milliseconds. Now, administrators can spend less time waiting when onboarding users or reorganizing access in large groups with many shared resources.
Security improvements
Passbolt 5.17.0 brings targeted security improvements and hardening measures resulting from internal assessments and external research.
- Safer Cookie Handling in Safari: Cookie management within the Safari extension is strengthened following insights from the recent Cure53 audit. Cookies are now more strictly isolated preventing them from being unintentionally exposed to other hosts
- Clipboard Auto-Clear Protection: Thanks to a report from external researcher Alex J, an edge case has been fixed where a malicious website could intercept, copy or cut events to cancel the clipboard-clearing timer. Copied secrets are now reliably cleared from the clipboard as intended.
- SCIM Token Enforcement (Pro Edition): Expired SCIM bearer tokens are now strictly rejected to prevent unauthorized ongoing access to provisioning endpoints. Administrators also receive proactive health checks and daily notifications, when the token is used and nearing expiration.
A dedicated security bulletin will be published soon. It will provide more details on each of the resolved issues, including their potential impact and how they were addressed.
Updating to Passbolt 5.17.0 is recommended to benefit from these security improvements.
Conclusion
Many thanks to everyone who provided feedback, reported bugs and contributed to making Passbolt better.
Changelog
API
Added
- PB-53318 As a user I can add passkeys as multifactor authentication provider
- PB-54953 As a user I can use passkeys as multifactor authenticator from the Passbolt mobile app
- PB-39607 As an administrator I can cleanup soft-delete active resources that no longer have an associated secret
- PB-54494 As an administrator I can configure SCIM admin token expiry and the near-expiry window
- PB-54498 Adds a healthcheck warning administrators when a SCIM admin token is nearing expiry
- PB-54499 As an administrator I get notified by email when a SCIM admin token is near expiry or has expired
- PB-55263 Adds an "Is encrypted for its recipient" data check in secrets
Fixed
- PB-54495 Adds a ScimTokenExpiryChecker service to compute SCIM admin token expiry state
- PB-54496 Rejects SCIM requests presenting an expired admin token at authentication time
- PB-54497 Adds a ScimUnauthenticatedResponseMiddleware returning a structured 401 payload on SCIM auth failure
- PB-53970 Flushes all users' MFA settings when an administrator disables MFA for the organization
- PB-54696 Shortens the TTL of mfa_setup and mfa_verify authentication tokens
- PB-54701 Enforces one active MFA ceremony handle per user
- PB-54828 Fixes a null type value in the ResourceTypes slug definition
- PB-54830 Adds an index on the users.username column to speed up user lookups
- PB-54831 Adds a composite index on scim_entries(scim_name, foreign_model) to speed up SCIM lookups
- PB-54832 Adds a retry loop to UserScimResource::create() to withstand concurrent SCIM writes
- PB-54833 Maps 500 responses from the SCIM endpoint to 429 with a Retry-After header on concurrency conflicts
- PB-54856 Reduces the number of queries inside the loop in FoldersRelationsSortService
- PB-54857 Adds a limit to isItemPersonal() when checking if an item is personal
- PB-54858 Improves setSecretRevisionInData() to not search the full collection each time
- PB-54980 Fixes the wrong CTA URL in offline mode emails
- PB-54990 Deactivates all authentication tokens on user soft-delete
- PB-55138 Reduces PASSBOLT_AUTH_JWT_REFRESH_TOKEN expiry to 1 hour
Security
- PB-53564 Excludes authentication tokens from the SQL dump command
- PB-54638 Fixes blind SSRF via avatar upload (AL-02)
- PB-54640 Fixes MFA brute-force limiter not counting failed TOTP codes submitted to the JSON endpoint (AL-01)
- PB-54703 Fixes SSRF egress guard bypass in SSO provider URL validation (AS-01)
- PB-55268 Fixes braces security vulnerability GHSA-vfj7-8cjw-p6xm (CVSS 3.1 HIGH)
Browser extension
Added
- PB-53327 Include group membership changes in the permission drift calculation before saving
- PB-53450 AUTOFILL - WP 2.0 - Create the orphanDictionary for the DOM extraction
- PB-53451 Add OrphanFieldPredicates class to check whether an element is a button
- PB-53452 AUTOFILL - WP 2.2 - Create the FieldVisibilityService to avoid detection of hidden inputs
- PB-53460 Add FormExtractionService to gather forms with viewable text fields
- PB-53461 AUTOFILL - WP 2.4 - Create the OrphanFieldsExtractionService to extract build the orphan forms
- PB-53462 Create NestedFormExtractionService
- PB-53464 Rework InFormCredentialsFormField
- PB-53465 AUTOFILL - WP 2.8 - Update the InFormManager to use the new extraction logic
- PB-53466 AUTOFILL - WP 3.0 - Create the TextNormalizer as an helper to infer on extracted text
- PB-53480 AUTOFILL - WP 3.1 - Create the ScrapingDictionary to handle scraping constants
- PB-53482 AUTOFILL - WP 3.2 - Create the ScrapingIdentity to support identifier after scraping
- PB-53483 AUTOFILL - WP 3.3 - Create the ScrapingCache object
- PB-53484 AUTOFILL - WP 3.4 - Create the PageScraperHelpers to group helpers used for scraping
- PB-53485 AUTOFILL - WP 3.5 - Create the LabelScraper to handle the label logic extraction
- PB-53486 AUTOFILL - WP 3.6 - Create the FieldScraper to handle the field extraction
- PB-53487 AUTOFILL - WP 3.7 - Create the FormScraper to extract information from form
- PB-53488 AUTOFILL - WP 3.8 - Create the FieldQualifier to detect the type of field scraped
- PB-53489 AUTOFILL - WP 3.9 - Create the PageScraper
- PB-53980 PCD - improve PCD on move operations
- PB-54162 AUTOFILL - WP 4.0 Create keywordsDictionary for classification
- PB-54163 AUTOFILL - WP 4.1 Create taxonomy for classification
- PB-54165 AUTOFILL - WP 4.2 Create KeywordMatchingService
- PB-54167 AUTOFILL - WP 4.3 Create FieldFeatureService
- PB-54168 AUTOFILL - WP 4.4 Create FormClassificationService
- PB-54171 AUTOFILL - WP 4.5 Create SawfClassificationService
- PB-54172 AUTOFILL - WP 4.6 Create PasswordRoleResolutionService
- PB-54173 AUTOFILL - WP 4.7 Create FieldsRationalizationService
- PB-54184 AUTOFILL - WP 4.8 Create SegmentedOtpResolutionService
- PB-54185 AUTOFILL - WP 4.9 Create ClassificationService
- PB-54336 AUTOFILL - WP 4.10 Create PageClassificationService
- PB-54337 AUTOFILL - WP 4.11 Connect the new service to the fill plan
- PB-54346 AUTOFILL - Fill not working on modal when z index is high
- PB-54374 AUTOFILL - Call-to-action missing on first focus for shadow-DOM fields
- PB-54344 AUTOFILL - Autocomplete should not block when it not valid
- PB-54500 Quick access: list PIN code resources
- PB-54502 Quick access: display PIN code in the resource view page
- PB-54530 AUTOFILL is not working for input length attribute
- PB-54571 Add the Passkeys provider toggle to the MFA administration page
- PB-54596 Implement the restartable WebAuthn setup ceremony
- PB-54608 OFM - PIN Code as offline available resource
- PB-54706 Show the Passkeys card in the user MFA provider overview
- PB-54707 Add the passkey authenticator icon set and AAGUID mapping to the styleguide
- PB-54709 Add the passkey registration flow to the Passkeys settings page
- PB-54710 Implement the WebAuthn MFA verification page as a styleguide React application
- PB-54759 BEST - WP 1.1 - Implement ScimEntity for Healthcheck
- PB-54760 BEST - WP 1.2 - Update HealthcheckEntity to handle the new ScimEntity
- PB-54761 BEST - WP 1.3 - Update DisplayScimSettingsAdministration to handle the new expiry behaviour
- PB-55047 Prune fields nested in forms deeper than the one evaluated
- PB-55050 False positive on first name and inform menu blinking
- PB-55099 Fix add user to group progress dialog for offscreen
- PB-55115 Implement the delegated WebAuthn MFA verification page for the mobile applications
Fixed
- PB-53265 Autocomplete fails in share dialog when custom email validator is on
- PB-54103 Fix null reference on storage change event
- PB-54531 Editing resources in a group-view doesn't update the grid
- PB-54764 OFM button not presented to eligible authenticated user with mfa required and API unavailable
- PB-54790 Prevent potential issue with TOTP autofill
- PB-54818 Offline mode plane icon stroke width should be 1.5px instead of 2px
- PB-54841 Fix quickaccess tab not opening when an account is not configured
- PB-54976 AUTOFILL - Plex CTA is blinking
- PB-55046 AUTOFILL - agoda email is not fillable
- PB-55048 AUTOFILL - Focus on a input should keep the CTA
- PB-55136 AUTOFILL - confirm password should be filled on a form
- PB-55155 AUTOFILL - Fix ant design search input is not working
Security
- PB-52830 restrict retrieved cookie on Safari to what a browser would normally get back
- PB-52831 Ensures Safari does not accept unexpected redirection to avoid cookie leakage
- PB-52832 Fix parameter name in sanitizeUrl function
- PB-53545 Major upgrade for yargs (Low)
- PB-53942 Fix image-size GHSA-5p2g-fcmc-qvqq - HIGH CVSS4.0
- PB-54648 Fix adm-zip GHSA-vwc7-r8mq-g2x9 - CVSS4.0 MEDIUM
- PB-54751 Major upgrade for @noble/hashes (Low) - passbolt-styleguide
- PB-55262 Fix undici multiple CVEs - CVSS3.1 HIGH
- PB-55264 Fix axios multiple CVEs - CVSS3.1 HGH
- PB-55267 Fix braces-expansion multiple CVEs - CVSS3.1 HIGH
- PB-55268 Fix braces GHSA-vfj7-8cjw-p6xm - CVSS3.1 HIGH
- PB-55274 Fix shell-quote GHSA-pqg4-j6r4-53mv - CVSS4.0 CRITICAL
- PB-55276 Fix fast-uri multiple CVEs - CVSS3.1 HIGH
- PB-55277 Fix source-map-js GHSA-68fv-2mgg-jv7q - CVSS4.0 HIGH
- PB-55279 Fix i18next-http-backend GHSA-xvq9-wjp8-hwqf - CVSS3.1 LOW
- PB-55293 Fix joi multiple CVEs - CVSS4.0 HIGH
- PB-55295 Fix probe-image-size GHSA-gjj5-9665-rwrc - CVSS3.1 HIGH
- PB-54842 clipboard auto-clear bypass via untrusted copy/cut DOM event
Maintenance
- PB-49117 optimise tab retrieval by id
- PB-52127 SAF - Reactivate avatar handling from client
- PB-54525 Product naming convention for Group Manager instead of Group Admin